
Citrix Virtual Apps & Desktop 7 2411

Citrix have released a new version of Citrix Virtual Apps and Desktop 7 2411 CR.
Citrix CVAD Release 7 2411 CR is now available for download,20 December, 2024.
Citrix Virtual Apps & Desktop 7 2411 is a CR release. CR is supported 1 year.
Citrix raises the bar of for user experience and new product release of following technologies:
- WebStudio 2411
- Director 2411
- Citrix Licensing 11.17.2 build 51000
- Virtual Delivery Agents 2411 for Windows ServerOS and ClientOS
- Virtual Delivery Agent 2411 for Linux
- Virtual Desktop Agent 2411 for MacOS
- Citrix Federated Authentication Service 2411
- Citrix Provisioning 2411
- Profile Management 2411
- Workspace Environment Management 2411
- Session Recording 2411
- Citrix Secure Private Access 2411
- Citrix Virtual Apps and Desktop Service (Oct-Dec 2024)
- Workspace App 2411 for Windows
- Workspace App 2411 for Linux
- Workspace App 2411 for Chrome
- Workspace App 2411 for Android
- Workspace App 2411 for MacOS
- Workspace App 2411 for HTML5
- Workspace App 2411 for ChromeOS
What’s new in Citrix Virtual Apps and Desktop 7 2411
HDX Connectivity
HDX Direct – Internal
HDX Direct for internal users is generally available. It allows internal client devices to establish a secure direct connection with the session host if direct communication is possible. For more information, see HDX Direct.
Graphics
Interactivity optimizations
Add default optimizations that prioritize interactivity over bandwidth in certain use cases. This ensures faster responsiveness in real-time scenarios, providing a smoother user experience. There’s no configuration needed as it’s enabled by default.
Maximum video buffer size setting
For VDA version 2311 and later, the Maximum Video Buffer Size setting now supports any value in kilobytes. If not set or set to 0, the default is no maximum. In VDA 2308 and earlier, the range remains 128 to 4,194,303 KB with a default of 65,536 KB.Citrix recommends leaving the default for VDA 2311 and later, as HDX dynamically allocates the necessary memory based on session needs, supporting higher resolutions and multiple monitors. For more information, see Display memory limit.
Optimized content sharing for teams and other platforms
This setting allows you to configure optimized application and desktop sharing for Microsoft Teams, Zoom, Webex, and other video conferencing platforms using the Citrix VCSDK. It supports App and Desktop Sharing on Windows, Mac, Linux, and VDA environments. By default, both sharing options are enabled and can be customized. This setting is specific to UC applications and overrides the VDA UseWsProvider registry key when configured. For more information, see Optimized Content Sharing for Teams and other platforms.
Enhanced startup application support for seamless sessions
In Citrix Virtual Apps and Desktops 2212 and later, Seamless applications now process Windows startup applications like desktop sessions. The Shell Launcher (ShellAppRuntime.exe) launches programs from the user’s Run key, such as OneDrive and Microsoft Teams, alongside Seamless apps, improving session management and startup consistency. For more information, see Seamless and startup applications.
Multimedia
Updated HDX optimized webcam display names for improved UI clarity
HDX optimized webcams have been updated with a shorter prefix in their display name from “Citrix HDX Webcam – [webcam name]” to “HDX – [webcam name]” to prevent name truncation in UI dropdowns. USB redirected webcams will keep their current naming convention i.e. excludes the prefix in their display name and simply “[webcam name]”. This update aims to standardize webcam names and reduce truncation across VDA platforms.
Virtual channel plugin manager
The Virtual channel plugin manager can detect when the end-user on the VDA launches a third-party application for e.g., New Microsoft Teams, check if its respective VDI plug-in is already installed on the endpoint, and prompt the user to install the plugin if it is not. The prompt would download and automatically install the plugin with the end-user’s permission.
Supported applications: New Microsoft Teams
For more information, see Virtual channel plugin manager.
Devices
Scanning on non-windows client platforms – SANE Redirection
You can now scan documents from TWAIN applications on ChromeOS endpoints. Scanning requests are redirected to the local scanner, and files are transferred to the VDA once the scan is complete, offering seamless integration for ChromeOS users. For more information, see Scanning on non-windows client platforms – SANE Redirection
Web Studio
Clarity on dependent policies
Some settings are dependent on other settings. For example, a child setting might be configured, but if its parent setting is not enabled, the child setting configured does not take effect. The dependencies were not clear before. Starting with this release, clarity is provided on which are the parent policies that must be configured first before you can configure the child policies. For more information, see Policy settings.
Multi-select policies
You can now select multiple policies and checkout the following enhancements:
- Click a policy row: If you click a policy row, the actions bar at the top shows actions of a single policy. The details pane at the bottom provides information about the policy.
- Select the check boxes of multiple policies: If you select the check boxes of multiple policies whose statuses are either enabled or disabled, then the actions bar at the top shows actions of multiple policies. The details pane at the bottom displays the number of policies selected.
NOTE:
After you select multiple policies, you can view the details of another single policy by clicking the row of that policy. This action does not clear the previously selected policies. However, the right-click action does not display the actions for that policy row.
Backup and restore using Web Studio
You can now use the Backup and Restore node available in Web Studio. This feature enables you to create on-demand and scheduled backups and restore deleted applications, policies, and more. For more information, see Backup and Restore using Web Studio.
Azure SQL support
You can now host Citrix Virtual Apps and Desktops databases on Azure SQL Managed Instance. To support this capacity, we’ve updated the following UIs:
- Citrix Site Manager wizard: Enables you to create databases on Azure SQL Managed Instance.
- Settings page in Web Studio: Enables you to change the locations of databases hosted on Azure SQL. For more information, see Set up databases and Change database locations.
Set a default domain name for the Studio login page
We’ve introduced a feature that allows you to configure the domain name that auto-populates the Domain field on the Studio login page. This enhancement streamlines the login process and reduces input errors. For more information, see Set the default domain name.
Image management is now Generally Available
Image management functionality is now generally available for Azure and VMware virtualization environments. Also, the Images node now allows you to share image versions across hosting units within the same hosting connection in Azure and VMware virtualization environments. This implementation ensures consistency and uniformity of images across different host units, enhancing deployment flexibility and operational efficiency. You can also use PowerShell commands to achieve this goal. For more information, see Image Management.
Support for provisioning non-domain-joined VDAs on Web Studio
With this feature, MCS supports provisioning of non-domain-joined VMs with customer managed Citrix Virtual Apps and Desktops deployment. For information, see Identity pool of non-domain-joined machine identity.
Option to update Write-back cache setting post creation for Machine Creation Services (MCS) catalogs in the Google Cloud Platform
You now have the option to update the memory and disk cache size of the Write-back cache, when Machine Creation Services (MCS) Storage Optimization (MCSIO) is enabled, after the catalog is created for MCS catalogs in the Google Cloud Platform. For more information, see Create a machine catalog using Web Studio.
Enroll machines of hybrid AAD joined type into Microsoft Intune for co-management
During machine catalog creation, you can now enroll machines of the Hybrid AAD joined type into Microsoft Intune (with Configuration Manager) for co-management. This feature applies to single and multi-session, persistent and non-persistent VMs and on all hypervisors and cloud services, ensuring uniform device management across your infrastructure. This feature is applicable only to VDA version 2407 and later. For more information, see Hybrid Azure AD joined catalogs enrolled in Microsoft Intune and Create Hybrid Azure AD joined catalogs enrolled in Microsoft Intune.
Multiple NICs support for Azure VMs
With Web Studio, you can now create Azure VMs with multiple NICs. A VM’s maximum NIC count is determined by the machine size setting while its actual NIC count allowed is defined by the machine profile setting. For more information, see Create machine catalogs.
Azure catalogs support for inheriting DES settings from master images
Previously, Web Studio set the Azure catalogs’ default DES settings only based on machine profiles. With this enhancement, if no machine profile is selected or if the profile specifies a Platform Managed Key (PMK), Web Studio now sets an Azure catalog’s default DES settings directly based on the master image. For more information, see Create a machine catalog using an Azure Resource Manager image in Web Studio.
Support for delivering packaged applications in FlexApp format
With Web Studio, you can now upload FlexApp packaged applications to Citrix Cloud and deliver them to your users. For more information, see App packages.
Enhanced application publishing with file type association
We’ve added an option, File Type Association, for publishing applications in Web Studio. This feature enables you to specify and manage file extensions for applications when publishing them:
- When you add local app access applications, this option appears in the left pane.
- When you add an application for delivery or application groups, this option is accessible through the Properties menu of the application.
Support for choosing a power management connection for a Remote PC Access catalog
Previously, you could use Studio to create a Wake on LAN host connection to your resource location (selecting Remote PC Wake on LAN as the connection type). However, PowerShell was your only choice to associate that connection with a Remote PC Access catalog. You can now use Studio to achieve that. For more information, see Configure Wake on LAN using Studio.
Support for showing the status of the provisioning process
In Web Studio, when creating a machine catalog, you can now view the status of the catalog’s provisioning process. You can see which step the provisioning process is currently in and how many steps are yet to complete.
Delivery group details view enhanced with policy information
We’ve enhanced the Details view for Delivery Groups by adding a dedicated tab that shows policies assigned to the selected group. This improvement simplifies policy management, configuration, and troubleshooting for delivery groups by providing quick access to relevant policy information.
Policies UI improved for better user experience
We’ve enhanced the UI design for the Policies node to improve its overall usability and functionality. Detailed improvements include:
- Full screen for creation and editing UIs. Full-screen mode is now used for an improved and more efficient creation and editing experience on the Policies node.
- Simplified setting filtering. A dropdown list for supported VDA versions is now available under the Current settings only filter, allowing you to filter settings based on VDA versions.
- Enhanced setting categorization. When you select multiple settings, the number of settings chosen now appears next to the relevant categories and sub-categories in the left pane. This improvement helps you quickly identify the category and sub-categories to which each selected setting belongs, streamlining your policy management.

Simplified printer configuration experience
We’ve enhanced Studio to make printer configuration easier. In addition to entering a printer‘s UNC path, you can now browse for printers across your network or on specified printer servers. This enhancement provides a more intuitive and reliable way to configure printers. Additionally, a new option now lets you use credentials other than your username and password when browsing for printers on printer servers. For more information, see Default printer, Printer assignment, and Session printers.
Export function extended to all management nodes
You can now export records from the main view of any management node in Web Studio to a CSV file. Note the following:
- The Export icon is disabled while data is loading, except for the Search and Applications nodes.
- For nodes with the Columns to Display function, exported data includes only selected columns.
Enhanced default view settings for machine catalogs, delivery groups, and applications
We’ve introduced new default view options for Machine Catalogs, Delivery Groups, and Applications, offering greater flexibility and customization:
- Default view selection. Previously, those nodes defaulted to a folder view, which was suitable for organizations using folder-based management structures. With the introduction of a Folder icon on the action bar, you can now switch between folder view and list view as your preferred default view.
- Improved folder view. The View all toggle now retains your last selection when you sign back in. If previously turned off, it will remain off, with the root folder selected and the first-level sub-folders expanded.
Data caching for the Details tab on Web Studio nodes
We’ve introduced data caching for the Details tab on all management nodes in Web Studio. This enhancement significantly reduces the data load time for the Details tabs, improving the overall user experience.
Support for adding notes for maintenance mode
You can now add notes when placing a machine, delivery group, or connection into maintenance mode. Those notes are visible in the Maintenance reason field of the Details pane, helping you and other administrators understand the reason for maintenance.
Citrix Studio
Deprecation of MMC-based Studio
Starting with 2411, MMC-based Studio is deprecated and will be removed in future releases. This means no new features will be added, and future updates will focus only on stability and security. We recommend transitioning to Web Studio, which offers the same features as MMC-based Studio, along with a modern interface and enhanced capabilities.
Citrix Director
Least used and unused published apps report
The Applications page now offers detailed usage information for published apps accessed through the Citrix Workspace app, empowering administrators to optimize app management and resource allocation.
This feature helps in understanding the application usage patterns within the organization and enables customers to make data-driven decisions to help make their Citrix deployments more efficient.
NOTE:
This feature is available only for the platinum-licensed sites.
The enhanced Applications page includes a usage section that shows the following:
- Total published apps: Identifies the total number of published apps.
- Least used apps: Helps to make informed decisions about retaining or removing rarely used apps, optimizing resource allocation, and license management. This section lists the following:
- Distinct users in the last 30 days
- Total launches
- Peak concurrent instances
- Trend chart: View a graph showing distinct users over time.
- Not used apps: Helps to identify unused apps to free up memory, configuration resources, and potentially save on licensing costs. This section lists the name of the apps, the corresponding delivery group, and the state of the app.
You can also use the Export option to export the data in the Least used and Not used sections.
NOTE:
Currently, only published apps (desktop apps in Citrix Workspace app) are included in this enhancement.

For more information, see the Least used and unused published apps report documentation.
Enhancement to advanced alert policies
Alerts related to Infrastructure monitoring, which were previously known as Infrastructure policies, are now part of Advanced Alert Policies.
You can select the dependent services based on the selected data source. You can create alerts for Cloud Connectors too.
NOTE:
The existing Infrastructure policies created for Provisioning Service and StoreFront are migrated to the Advanced alert policies section.
For more information, see Advanced alert policies.
Bulk alert dismissal
This feature aims to optimize the alert management process for administrators by providing more flexibility and reducing alert fatigue. It allows administrators to bulk dismiss alerts by time, type or category, making it easier to manage alerts, especially during maintenance modes or when dealing with alerts from hypervisors and other environments.
By allowing bulk dismissal of alerts, administrators can manage their workload more efficiently and avoid being overwhelmed by a high volume of alerts.
For more information, see Bulk alert dismissal.
Webhook configuration using PowerShell SDK
The Webhook Configuration feature using the PowerShell SDK allows administrators to create, modify, delete, and list webhook profiles. This feature provides flexibility in configuring webhooks by allowing the specification of headers, authentication types, content types, payloads, and webhook URLs.
NOTE:
The supported payload format is text and the end user must enable text in their webhook.
For more information, see Webhook configuration using PowerShell SDK.
Improvement to Workload rightsizing
The Workload rightsizing (formerly Infrastructure Rightsizing) tab now includes an option to identify power users. This feature allows you to export the details of power users.
NOTE:
This feature is available only for single-session OS delivery groups.
The Export data includes User Name, Total Session Count, Average Session Duration (Mins), Peak CPU Usage (%), and Peak Memory Usage (%).
This enhancement provides valuable insights into resource utilization and helps in optimizing infrastructure costs by ensuring efficient resource allocation based on user behavior.
For more information, see the Workload rightsizing page.
Machine net active usage
The Workload rightsizing page now includes detailed insights into machine net active usage, providing the following details:
- Percentage of net active usage
- Average machine uptime
- No session time
- Idle time
- Disconnected time
This feature allows you to see detailed machine usage information, enabling you to optimize costs accordingly.
For more information, see Workload rightsizing.
Cost savings by optimizing storage usage [Preview]
The Cost savings page now provides visibility into the amount of savings achieved through storage optimization when machines are powered off. Previously, only compute-related cost savings were displayed. This enhancement includes the following two types of storage savings:
- Write-back Disk: Savings from deleting the write-back disk when a non-persistent machine is powered off.
- OS Disk: Savings from downgrading the OS disk from Premium to Standard HDD when any machine is shut down.
Prerequisite:
- Autoscale must be enabled to optimize compute costs. For more information, see Get started with Autoscale.
- Change the storage type to a lower tier when a VM is shut down to optimize storage costs. For more information, see Change the storage type to a lower tier when a VM is shut down documentation.
- This feature is applicable only to Azure machines.
This enhancement includes the following:
- A report detailing storage savings from machine power-off (Autoscale or user-initiated) is now available in the Estimated infrastructure savings section.
- Total savings calculations now incorporate both compute and storage savings, broken down by source (Autoscale or user action). The historical trend graph now visually distinguishes between compute and storage savings, and a tooltip provides further details on hover.
- The Catalog details section now includes Compute Cost Per Hour and Storage Cost Per Hour.
For more information, see Cost savings [Preview].
Cost summary [Preview]
The Cost summary page provides a comprehensive summary of the expenses associated with running the Citrix environment. With this enhancement, you gain visibility into the following:
- The overall cost per user
- Cost of delivering virtualization by the chosen Workload providers, desktop types, and VM series sets
This page offers:
- Insight into the cost of delivering a virtualized app or desktop to a user The amount saved
- Information on costs and savings categorized by
- Platform provider
- OS type
- Desktop type
- VM series
NOTE:
The Cost summary page is available only if the site has been running for at least 15 days in a month.
For more information, see the Cost summary page.
Export data from the Cost optimization page
You can export the data on the Cost optimization page using the data integration and ODATA queries. To export data, you can use one of the following options:
- Setup data integration – You can integrate Cost optimization data with the Monitor Service API using which you can collect the data for troubleshooting and triaging the issues. For more information, see the Integrations and data exports page.
- ODATA queries for cost optimization – You can use the available sample ODATA queries on the Cost optimization page to export data.
For more information, see Export data.
Delivery Controller monitoring [Preview]
The Delivery Controller component is now added to the Infrastructure Monitoring dashboard, and the delivery controllers are automatically onboarded when connected to the Citrix Virtual Apps and Desktops site for on-premises deployment.
This feature enables administrators to monitor the health of Delivery Controllers using a single dashboard view and proactively configure alerts.
NOTE:
The
CitrixInfraMonitor.msiis not required to be installed for monitoring Delivery Controllers.
Benefits:
- Comprehensive monitoring: Visibility into critical health indicators for the Delivery Controller such as License Server and certificate validity.
- Configurable alerts: You can configure alerts on health metrics of interest, define severity, and scopes for admins to receive detailed alerts according to the alert configuration.
To monitor the Delivery Controller, click the Infrastructure tab on Director. The Infrastructure Monitoringpage opens:

For more information, see Delivery Controller health metrics.
Connecting Citrix components from the UI [Preview]
Admins can use the Monitor UI to register their Citrix components for Infrastructure Monitoring. After installing Citrixinframonitor.msi, you can use the UI-based workflow to complete the registration process without needing to use PowerShell commands. This enhancement simplifies the process of registering, deregistering, and updating Citrix components
The new Connect Citrix Components page allows you to manage connections between Citrix components and the Citrix DaaS site. You can also view the available connections from Provisioning Service, StoreFront, and Cloud Connector on this page.
NOTE:
Delivery controllers are automatically onboarded for monitoring.
These updates streamline the management and integration of Citrix components, making it easier to maintain and upgrade your infrastructure.
For more information, see Manage connections.
Enhancement to Trends page
The Trends page now features two new banners linking to the Cost optimization page, providing quicker access to cost-saving information and reports. The Machine Usage tab now includes links to Estimated Savings and Savings report, while the Resource Utilization tab offers a link to Workload rightsizing. These enhancements streamline navigation and improve visibility, enabling users to make data-driven decisions for cost optimization.
For more information, see the Available trends page.
Improved Performance Metrics panel
The Performance Metrics panel has an enhanced visualization of the historical data metrics. When you click the Session Performance tab, along with the last 15-minutes data, you can view the last 48 hours data for ICARTT and ICA Latency. This enhancement helps to reduce mean time for resolution by enabling admins to triage issues even though the session was terminated in the last 48 hours. For more information, see the Performance Metrics section.
Update to Session Performance tab
The Session Topology section of the Session Performance tab is enhanced to include the following:
- Protocol – Displays the MTU value for the EDT protocol. For example: Single-stream: EDT (MTU = 1500) Multi-stream: EDT (MTU stream IDs 0=1500, 1=1500)
- Microsoft Teams – Displays whether HDX optimized or not HDX optimized
- HDX Connection Type – Displays the HDX connection type. For example: HDX, HDX Direct, and Rendezvous
- Frames Per Second provide information on:
- Input Frames Per Second
- Output Frames Per Second
- Endpoint metrics which exist in the Citrix Workspace app for Windows:
- Public IP address
- Internet Service Provider
- Location such as country or city
- Whether the Citrix Workspace app session is opened in native app or browser (HTML5)
- Accessed using Workspace or StoreFront
- Resource utilization such as CPU %, Memory %, and GPU (Overall %)
- Network latency
This enhancement helps to troubleshoot session issues quickly.
For more information, see Session Performance metrics.
Enhancement to Filters tab
With this release, the following extra filters are added to the Sessions tab.
- All – Displays all sessions
- Active, Connected, and Disconnected – Displays only the active, connected, and disconnected sessions.
- Ended – Displays only the sessions that have ended within the last 48 hours. The default filter is Active, Connected, and Disconnected.
User experience improvement for alerts and usability
In response to customer enhancement requests, the user experience has been improved by avoiding the display of machines at maximum load as an error. This change is beneficial for customers using Vertical Load Balancing, where maximum load is expected.
This improvement removes the maximum load data from the dashboard, filter, and trends pages. To view machines that reach maximum load, you can use the Monitor OData API to get all machines’ status. You can also use the Director UI to view the machines at maximum load.
To view machines at maximum load from Director UI:
- Navigate to the Filters tab.
- Select the default filter – All Machines.
- Ensure that no other filters are applied.
- Sort by Failure Type.

This feature allows viewing machines at maximum load without them being alerted as errors.
Enhancement to ended session [Preview]
In the ended session (formerly historical session), the Session Performance tab shows data for the last 48 hours. Also, you can view the Session Logon tab for the ended session.
For more information, see Diagnose ended user sessions [Preview].
Additional details on the Session Topology view for Secure Private Access apps (Preview)
You can now view the following extra details in the Session Topology view for Secure Private Access apps. This change applies to both Web and SaaS apps, as well as TCP/UDP apps.
Endpoint:
- Endpoint type: This can be either the Secure Access Agent or Citrix Workspace app.
- Access details: View how the endpoint is accessed, whether through StoreFront or Citrix Workspace app.
- Endpoint OS: For example, Windows.
- Location type: Indicates whether the location is internal or external.
Resource Location:
NOTE:
Resource location is applicable only for Web and SaaS apps.
- Number of enumerated applications: Displays the number of enumerated applications and the store URL.
- Access method: Indicates whether the endpoint is accessed through StoreFront or Citrix Workspace app.
Secure Private Access:
- Configured policies: Displays the number of configured policies.
- FQDN plug-in: Shows the FQDN of the agent that served the request.
Web and SaaS App / Client-Server App (TCP/UDP):
- App name: The name of the app.
- Top level URL: For Web or SaaS apps, the URL of the published app is displayed. For TCP/UDP apps, the protocol IP address of the app is displayed.
- App type: Indicates whether the app is a Web or SaaS app, or a TCP/UDP app.
- App publishing type: Indicates whether the app is published externally or internally.
For more information, see the Session Topology view for Secure Private Access apps section.
Enhanced Activity Manager for TCP or UDP apps (Preview)
You can now view enumerated application details for TCP or UDP apps on the Activity Manager under Available Apps. Also, you can view the resource URL and the type of accessed resource (TCP or UDP). This enhancement aids in troubleshooting Secure Private Access issues.
For more information, see the Session Topology view for Secure Private Access apps section.
Scout
Scout supports TraceLogging provider
Previously, Scout supported only the Windows performance provider, which required extra decoding files and traced only sessions and events from a single session for the same provider.
With this release, Scout now supports the TraceLogging provider. This provider does not require extra decoding files and can enable and receive events from up to eight trace sessions for the same provider. This feature is enabled by default.
Command-line interfaces for Scout functionalities
You can now use command-line interfaces for Scout functionalities, enabling you to collect needed logs and data without opening the Scout UI. This feature provides convenience for advanced users to automate the log or trace process locally or remotely for target machines or sites. This feature is enabled by default.
Commands are added for the following functionalities:
- Help
- Collect diagnostics
- Start and stop trace
- List session
- Start and stop CDC
NOTE:
When running the remote trace session, the new telemetry version must be installed on both VDA and DDC. This installation is required because the Scout command line is supported starting from Citrix Virtual Apps and Desktops version 2411, and older versions of
TelemetryServicedo not support this feature.
For more information, see Command-line interfaces for Scout functionalities.
Machine Creation Services (MCS)
Support for creating preformatted WBC disk catalogs in Azure
With this feature, in Azure virtualization environments, you are able to utilize a preformatted WBC disk for newly created catalogs. This action significantly reduces the time required to start each VM of an MCS or MCS provisioned Citrix Provisioning machine catalog. To implement this functionality, create an Azure catalog with WBC enabled and include an additional custom property PreformatWriteBackCache as True.
You can update an existing catalog using the Set-ProvScheme command to update the WBC disk size.
This feature is compatible with the Image management workflow where MCS separates the mastering phase from the overall provisioning workflow. For more information, see Create a preformatted WBC disk catalog.
Delete WBC disk at shut down for MCS provisioned Citrix Provisioning catalogs
With this feature, you have the option to delete the write-back cache (WBC) disk at shutdown for MCS provisioned Citrix Provisioning catalogs in Azure. This implementation helps to save cost when you do not need a persistent WBC disk. This feature is also applicable to an existing catalog. For more information, see Delete WBC disk at shutdown for MCS provisioned Citrix Provisioning catalogs.
Support for multi-region snapshot of the disk or an image of the disk as master image in GCP
A snapshot or an image of a disk in GCP can be regional or multi-regional. Regional snapshots and disk images are tied to a particular region, example, us-central1, whereas multi-regional snapshots and disk images are tied to a geo-location, example, US. With this feature, you can use a multi-region snapshot of the OS disk or an image of the disk as master image input when creating MCS machine catalogs in GCP. You can see the list of all snapshots (both regional and multi-regional) under snapshots.folder location and disk images (both regional and multi-regional) under images.folder under hosting unit inventory path.
Support for NitroTPM and UEFI secure boot capability for MCS created AWS VM instances
With this feature, when creating a catalog in AWS environments, you can now select a master image (AMI) with NitroTPM and/or UEFI secure boot enabled. Accordingly, the provisioned VMs in the catalog are also enabled with NitroTPM and/or UEFI secure boot. This implementation ensures that the VMs are secured and trusted. For more information on NitroTPM and UEFI Secure Boot, see the AWS documentation. For creating a catalog enabled with NitroTPM and UEFI secure boot, see Enable NitroTPM and UEFI secure boot for VM instances.
Support for creating a network security group
With this feature, you can now create a Deny-All network security group for image preparation instead of requesting Citrix to create and modify a network security group automatically. Edit the custom properties of the hosting unit using a PowerShell command Set-Item to include the parameter NsgForPreparationto provide the Deny-All network security group. For more information on using the PowerShell command, see Use a pre-created network security group.
Support for using Azure temporary disk as a WBC disk for existing MCS machine catalogs
With this feature, you can now use Azure Temporary disk as a write-back cache (WBC) disk for existing MCS machine catalogs and existing VMs. Use the Set-ProvSchem PowerShell command to update existing catalogs. This implementation saves storage cost because Azure temporary disk is free of charge. For information on the steps, see Use temporary disk as WBC disk for existing catalogs and VMs.
Filter empty resource groups
With this feature, you can filter out empty resource groups while selecting a master image, machine profile, or prepared image during the machine catalog creation. You can do this using a PowerShell command Get-HypInventoryItem. For more information, see Filter empty resource groups.
Migration of persistent and non-persistent VMs in XenServer
With this feature, in the XenServer environment, you can migrate the following VM disks from one storage to another storage using the Move-ProvVMDisk PowerShell command.
- For persistent Full Clone VMs: OS Disk, Identity Disk, and non-MCS provisioned disks.
- For non-persistent VMs: OS Disk, Identity Disk, and Write-back Cache (WBC) disk.
For more information, see Storage migration of persistent and non-persistent VMs.
Validate configuration before creating an MCS machine catalog in AWS environment
With this feature, you can now validate configuration settings before creating an MCS machine catalog using the parameter -validate in New-ProvScheme command. After you run this PowerShell command with the parameter, you get an appropriate error message if there’s an incorrect parameter used or a parameter has conflict with another parameter. You can then use the error message to resolve the issue and successfully create an MCS machine catalog using PowerShell.
Currently, this feature is applicable to AWS, Azure, GCP, and VMware virtualization environments. For more information, see Validate configuration before creating an MCS machine catalog.
Repair the identity information of active computer accounts in SCVMM
In SCVMM environments, you can now reset the identity information of active computer accounts that have identity-related problems. You can choose to reset only the machine password and trust keys, or reset all configuration of the identity disk. This implementation is applicable to both persistent and non-persistent MCS machine catalogs. Currently, the feature is supported only for AWS, Azure, SCVMM, and VMware virtualization environments. For more information, see Repair the identity information of active computer accounts.
Support for on-demand capacity reservation in Azure
With this feature, you can create an MCS machine catalog of Azure VMs with on-demand capacity reservation using a machine profile (VM or template spec). This feature is applicable to persistent and non-persistent machine catalogs. You can update an existing machine catalog and existing VMs to have or remove on-demand capacity reservation.
For more information on Azure on-demand capacity reservation, see the Microsoft documentation On-demand Capacity Reservation. For information on creating and updating an MCS machine catalog with on-demand capacity reservation, see Create a catalog of on-demand capacity reservation VMs.
Support for placing WBC disk on the same storage location as OS disk
In XenServer, VMware, and SCVMM virtualization environments, MCS now places Write-back cache (WBC) disk on the same storage location as OS disk if you configure the available OS storage list the same as the available temporary storage list while creating a host connection.
This implementation helps to reduce the complexity in managing the OS and WBC disks.
For creating a host connection, see Create a connection and resources.
Support for multiple NICs per VM on Azure
Previously, in Azure environments, MCS supported only one Network Interface Card (NIC) per VM. With this feature, MCS now supports multiple NICs per VM. You can associate multiple NICs on a VM to multiple subnets, however, those subnets must be in the same virtual network (vNet). For more information, see Create or update a catalog with multiple NICs per VM.
Connect to Azure Sovereign Airgap cloud environment
With this feature, you can connect to Azure Sovereign Airgap cloud environments using a custom property DisableInstanceDiscovery while creating a host connection. The Azure Sovereign Airgap cloud environment is suitable for top-secret workloads that must be on segregated network domains. For more information on creating a host connection to the environment, see Connect to Azure Sovereign Airgap cloud environment.
Reboot schedules for hibernated VMs
With this feature, you can configure reboot schedules for hibernated VMs if the Delivery Group is hibernation enabled. In the reboot cycle, the VMs are resumed and, then shut down. The reboot schedule can be set as weekly, daily, monthly, and once. You can configure multiple schedules. Note that VMs resuming from hibernation can take few mins.
Citrix Licensing 11.17.2 build 51000
What’s new in the License Server version 11.17.2 build 51000
License Activation Service
Starting with build 11.17.2 build 51000 version, Citrix Licensing includes the License Activation Service (LAS). LAS is a cloud-based licensing solution which provides new modules for activating Citrix products, offering a seamless and modern approach to license management. For more information, see License Activation Service.
Enhanced security with TLS 1.2
We’ve enhanced our security by adopting a secure-by-design approach, now disabling protocols older than TLS 1.2 by default.
Virtual Delivery Agents (VDAs) 7 2411 for Windows Desktop/Server OS.
Virtual Delivery Agents (VDAs) 7 2411 for Linux
Improved session stability
The user session process (ctxgfx) is now decoupled from the ctxhdx service. Previously, an active or disconnected user session could be terminated if the ctxhdx service was restarted. With this update, the user session can now retain its state even if the ctxhdx service is restarted, thus improving the overall session stability.
This feature is enabled by default. If it has been disabled, you can re-enable it using the following command:
/opt/Citrix/VDA/bin/ctxreg create -k "HKLM\Software\Citrix\HDXSessionRecovery" -t "REG_DWORD" -v "EnableSessionRecovery" -d "0x1" --force
Support for Ubuntu 24.04, Debian 12.7, Debian 11.11, and SUSE 15.6
The Linux VDA now supports the following Linux distributions:
- Ubuntu 24.04
- Debian 12.7
- Debian 11.11
- SUSE 15.6
For more information about supported Linux distributions, see System requirements.
OpenJDK dependency upgraded from version 11 to version 17
In this release, the OpenJDK dependency has been upgraded from version 11 to version 17. OpenJDK 17 is automatically installed as a dependency when you install the Linux VDA. For more information, see Install the Linux VDA manually.
Enhanced PostgreSQL version support
The Linux VDA now supports the use of a custom PostgreSQL version, regardless of the version provided by your Linux distribution. We recommend you use a PostgreSQL version that is at least as recent as the one provided by your Linux distribution. To effectively use a custom version of PostgreSQL, ensure that /etc/xdl/db.conf is configured appropriately for the new version. For more information, see the database specification instructions in the installation articles, for example, Step 7: Specify a database to use and Step 1g: Install and specify a database to use.
Rootless Xorg
The Linux VDA now supports running Xorg with non-root user privileges, also known as “rootless” Xorg. Rootless Xorg is a significant security improvement over running as root. For more information, see Rootless Xorg.
Service account “ctxsrvr” is moved to a new location
Starting with this release, the Citrix service account “ctxsrvr” is moved from /home/ctxsrvr to /var/lib/ctxsrvr.
Enhanced file copy and paste feature
This release includes enhancements to the file copy and paste feature, aimed at supporting special characters in file names. For more information, see File copy and paste.
Improved cross-platform keyboard functionality
This release addresses issues with keyboard functionality when sharing sessions between the Linux VDA and the Windows VDA. For more information, see HDX screen sharing.
Improved webcam capability
This release includes several enhancements to webcam functionality:
- Improved webcam resolution and FPS negotiation during device creation.
- Optimized the webcam creation and removal process.
- Added support for in-session webcam service self-heal.
Support for PipeWire in Ubuntu 24.04
The Linux VDA now extends PipeWire support to Ubuntu 24.04, where it is the default audio service. For more information, see Audio features.
Support for multiple audio devices and loss tolerant mode for audio are now generally available
Support for multiple audio devices is now enabled by default. Loss tolerant mode for audio can now be enabled through a policy setting instead of the registry. For more information, see Audio features.
Audio quality enhancer for adaptive audio (preview)
Starting with version 2411, we have introduced the audio quality enhancer for adaptive audio as a preview feature. This enhancement effectively manages short periods of packet loss and disruptions by intelligently reconstructing audio from previous samples, thus preventing noticeable degradation in quality. Also, it adaptively recovers lost audio packets only when necessary. The audio quality enhancer enables and disables itself based on sustained changes in packet loss, optimizing audio playback and recording quality in both good and bad network conditions. For more information, see Audio features.
Support for more auto client reconnect policies
The Linux VDA now supports the following policies, in addition to the auto client reconnect policy, for controlling the automatic reconnection of sessions.
- Auto client reconnect authentication
- Auto client reconnect logging
- Auto client reconnect timeout
For detailed policy descriptions, see Auto client reconnect policy settings.
NOTE:
When auto client reconnect logging is enabled, the Linux VDA writes auto client reconnections directly to the system log. This behavior differs from Windows, where the logs are written to the event log.
For a list of policies that the Linux VDA supports, see Policy support list.
Virtual Desktop Agents (VDAs) 2411 for MacOS
Support for new macOS release and Mac devices running Apple Silicon M4:
- macOS sequoia 15.1
- macOS sequoia 15.2
- Apple Silicon M4 based Mac mini and MacBook Pro
For more information, see System Requirements.
Loss tolerant mode for audio
Audio is now supported over the Enlightened Data Transport (EDT) loss tolerant protocol.
This feature increases the user experience for real-time streaming when users are connecting through networks with high latency and packet loss.
When this feature is enabled, Adaptive Transport in Citrix Virtual Apps and Desktops uses the EDT loss tolerant transport protocol for a better audio experience.
This feature is disabled by default. For more information, see Loss tolerant mode for audio section.
Extend more Citrix Policies support for Auto Client Reconnect feature
This release extends two more Citrix Policies for Auto Client Reconnect(ACR):
- Auto client reconnect timeout
- Auto client reconnect authentication
For more information, see Policy Support List and Auto Client Reconnect.
Integration with Citrix Virtual Apps and Desktops 2411
This release has conducted full integration test with the latest release Citrix Virtual Apps and Desktops(CVAD) 2411
Citrix Federated Authentication Service 2411
Renew FAS authorization certificates without disruption to users
Previously, renewing FAS authorization certificates caused disruption to users. With this change, the process has been simplified and improved to no longer cause disruption to users. For more information, see Renew FAS authorization certificate.
Improved process for managing key storage with FAS
Previously, configuring where FAS private keys are stored was handled through the Citrix.Authentication.FederatedAuthenticationService.exe.config XML file. This has been a pain point to manage and the configuration is not preserved over FAS upgrades. With this change, PowerShell cmdlets are used for private key configuration. Configuration for user and RA certificate private keys is stored separately, further simplified, and preserved over upgrades. For more information, see Private key protection
Support for Elliptic Curve keys
Until now, FAS has only supported RSA keys for use in its certificates. With this change, FAS introduces support for ECC certificates. For more information, see Example 4 – Use Elliptic Curve keys.
For information about bug fixes, see Fixed issues.
Citrix Provisioning 2411
Support for creating Citrix Provisioning catalogs in VMware environments using Studio
With Studio, you can now create Citrix Provisioning catalogs in VMware environments. Previously, you had to switch between different consoles to provision and manage those catalogs. This feature simplifies the process, letting you perform provisioning and power management tasks entirely within Studio. For more information see, Create a Citrix Provisioning catalog in VMware environment using Studio.
Enhanced performance of Citrix Provisioning Configuration Wizard
The Citrix Provisioning Configuration Wizard no longer scans for all database instances, which can be time-consuming with many database instances. Instead, you can now enter the database instance to use, significantly improving the experience of creating new farms and joining an existing farm. For information, see Identify the farm.
Downgrade script available in Citrix Provisioning ISO
The Downgrade.ps1 script is now included in the Citrix Provisioning ISO. It is located under \Tools\Scripts folder. For information on downgrade, see Downgrade.
Enable or disable scrambling of licensing telemetry data
Considering the sensitivity of information sent in the license telemetry, Citrix Provisioning provides you an option to enable or disable scrambling of licensing telemetry data. Scrambling is enabled by default. However, you can disable scrambling using MCLI or PVS SnapIn commands. You can also generate a mapping report of scrambled values to clear text values covering any data uploaded in the last one year using PowerShell commands.
For information on disabling scrambling and generating a report, see Enable or disable scrambling of licensing telemetry data.
Support for validation of license server’s certificate
When you validate license server communication, the license server’s certificate must be valid and trusted. If the license server is using a self-signed certificate that is valid but not trusted, you are prompted to add trust for the certificate. If the hostname is invalid for the server certificate that is used to connect (hostname mismatch), supported hostnames are suggested. For more information on selecting the license server using the Configuration wizard, see Select the license server.
Improved Windows Memory Optimization Management
Citrix Provisioning Optimizers are now enhanced to enable Windows Memory Compression. You can select the Disable Windows SuperFetch option on the Edit Optimization Settings dialog and still have Windows Memory Compression feature.
Enhanced support for Windows Server Core
With this enhancement, you can do the following after installing Citrix Provisioning Server on Windows Server Core:
- BDM update from a remote console connected to a Citrix Provisioning Server
- Create target VMs using Citrix Virtual Apps and Desktops Setup Wizard using HDD BDM boot.
The Server Core option is a minimal installation as opposed to the installation of Server with Desktop Experience. The Windows Server core reduces the potential attack surface to critical infrastructure.
Delete WBC disk at shutdown for MCS provisioned Citrix Provisioning catalogs
With this feature, you have the option to delete the write-back cache (WBC) disk after you shut down the VM for MCS provisioned Citrix Provisioning catalogs in Azure. This implementation helps to save cost when you do not need a persistent WBC disk. This feature is also applicable to an existing catalog. For information on creating an MCS provisioned Citrix Provisioning catalogs in Azure with WBC disk as non-persistent, see Delete WBC disk at shutdown.
Support for Linux streaming target devices
For Linux streaming, the following operating systems supported:
- Ubuntu 22.04, 20.04
- Red Hat Enterprise Linux 9.4, 9.2, 8.10, 8.8
- Rocky Linux 9.4, 9.2, 8.10, 8.8
- SUSE Linux Enterprise Server 15 SP5
For more information, see Streaming Linux target devices.
Citrix Profile Management 2411
Support for machine-level redirections
With the App access control policy, you can now implement machine-level redirections for files, folders, registry keys, and registry values using rules. The use cases for this feature include:
- Implement data roaming. Redirect non-user-profile data to a file share, ensuring users can access the same data regardless of which machines they sign into.
- Enhance data protection. Redirect critical data to alternative locations or values, protecting it from unauthorized access.
- Customize the user experience. Tailor app experience based on specific requirements.
For more information, see Implement machine-level redirections.
App access control policy enhanced with assignment exclusions
You can now specify excluded users, machines, and processes when configuring rule assignments for the App access control policy. Previously, you could only assign rules to groups of users, machines, and processes. This enhancement lets you define exclusions within those groups, offering more precise control over rule enforcement. For more information, see Control access to applications and Implement machine-level redirections.
New policy for access control for redirected folders
By default, when you enable folder redirection policies for a user, the redirection target folders are accessible only to the user and the SYSTEM user. Previously, to grant other users access, you had to enable the Grant administrator permission policy. This policy grants members in the Local Administrators group access to the redirection target folders.
With a new policy, Users and groups to access redirection target paths, you can now grant specific domain users or groups Read & Execute permissions on the redirection target folders, eliminating the need to add them to the Local Administrators group. This policy enhances security by limiting permissions only to what is necessary. For more information, see Grant users access to redirected folders.
New policy for accelerating UWP app loading
With a new policy, Enable AppX package load acceleration, you can now accelerate the loading of UWP apps and improve their consistency in non-persistent environments.
By default, Windows stores UWP App registration information locally on each machine, which can be lost upon restart in non-persistent environments. With this policy enabled, Profile Management creates a VHDX container for each machine to store the UWP app registration data, speeding up user logon and preventing data loss on restarts. For more information, see Enable UWP app load acceleration.
New policies for notifying users when their profile size exceeds a quota
Citrix Profile Management now introduces two new policies to monitor the user profile size and notify users when it exceeds a quota:
- Notify user when profile size exceeds quota: Lets you set a quota for the user profile and notify users when their profile size exceeds it.
- Notification message when profile size exceeds quota: Lets you set the notification message users receive.
This feature helps prevent data loss by notifying users to manage their profile data before logging off. It applies only to the file-based profile solution. For more information, see Enable user notifications for exceeding the profile quota.
In-session failover support for profile streaming
Profile streaming now includes improved failover capabilities. When the Replicate user stores policy is enabled, if the active user store becomes unavailable, Profile Management automatically switches to an available store for subsequent streaming requests. This enhancement lets files and folders be streamed continuously after the failover, minimizing data disruptions.
This update applies to profile streaming for files, folders, and the pending area.
Citrix Workspace Environment Management 2411
his release includes the following new features and addresses issues to improve the user experience:
Log export
This feature allows you to export your infrastructure service and web console logs to third-party platforms like Grafana and Splunk. After configuration, your infrastructure service and web console logs are sent to the specified platform within one minute. You can also disable or delete the configuration at any time if you no longer need to export the logs. For more information, see Global configurations.
Support data export to Splunk
Previously, you were restricted only to Grafana when exporting agent reports to third-party platforms.
With this feature, you can now effortlessly export the data to Splunk as well.
For more information, see Export to third-party platform.
Integration of the WEM Health Check tool into the WEM Tool Hub
The WEM Health Check tool is now integrated and listed within the WEM Tool Hub Home page for ease of access and use. This tool runs checks on the WEM agent or infrastructure server and identifies potential issues with your WEM deployment. For more information, see WEM Health Check tool.
Support data export to third-party platforms for flexible management
Previously, you were restricted to exporting reports solely to cloud storage or local machines, hindering your ability to effectively analyze and monitor task outcomes.
With this feature, you can now effortlessly configure and export report data to third-party platforms such as Grafana. This enhancement helps to seamlessly integrate and utilize external analytics tools for comprehensive performance monitoring and analysis, whether automatically scheduled or manually initiated.
For more information, see Reports.
Profile Migration Tool in the WEM Tool Hub
With the new Profile Migration Tool, you can now migrate different types of profiles to the Citrix container-based profile solution. This feature simplifies the profile migration process, ensuring a smooth transition and minimal disruption to user workflows. The following types of profiles are supported:
- FSLogix profile container
- Citrix file-based solution
- Local profile
For more information, see Profile Migration Tool.
Support for testing the app access control rules
You can now validate app access control rules on the local machine before deploying in the testing or production environment. For more information, see Rule Generator for App Access Control.
Add new built-in scripted tasks to reduce operation efforts
Added more valuable built-in script tasks that help admins use built-in scripted tasks directly and reduce operation efforts. This feature resolves unregistered VDA issues and sets CDF trace configurations. For more information, see Scripted Tasks.
Configuring registry and GPO settings with a new registry value type
- REG_NONE registry value type is introduced for more customized configurations by providing a way to specify settings or parameters that do not fit into other predefined data categories, such as, strings, integers, or binary data. You can use this flexibility to handle unique or specialized configurations.
- REG_NONE registry value type supports the following functions:
- In creating/updating registry entry action
- In creating/updating registry entry-based GPO action
- When importing a registry entry-based GPO
- On the agent side
- For legacy console
- For backup and restore from the web console and the legacy console
- For more information, see Create a GPO and Import Group Policy settings.
View a GPO
You can now view the WEM Group Policy settings. GPO summaries in read-only mode without editing the GPO. This implementation eliminates the risk of misconfiguration while reviewing the existing settings.
For more information, see Registry-based settings.
Selective WEM reset feature
WEM is enhanced to selectively reset WEM actions tracking cache. When you enable Allow Users to reset Cached Actions, the Reset Cached Actions is turned on. On clicking it, a new wizard gets displayed and then you can choose the cached actions that need a reset. This enhancement enables you to reset the process history for JSON files or the user group policy objects. After the reset, the actions get processed during the subsequent user logons.
Group policy migration to WEM
- You can now use the Group policy migration to migrate Group policy preferences that cause slow sign-ons into WEM actions to improve your sign-on experience. In the WEM Tool Hub, you can begin the migration workflow either within a logon duration report, while viewing GPO processing times, or from the Group Policy Migration Tool. This tool allows you to scan for currently applied GPOs. You can select from the listed items supported for migration. Selected items are exported as a ZIP file to the local machine, which is later imported as WEM actions. This feature is enhanced to guide you through the process of creating an assignment group with the exported settings, and also assign the group to the respective user.
- For more information, see Group Policy Migration Tool.
Introducing new insights to monitor and diagnose logon duration
This enhancement introduces profile container and GPP processing insights to monitor and diagnose logon duration. This feature enables you to identify the possible issues, which may cause slow logon and to also provide recommendations to resolve issues.
For more information, see Windows Logon analysis.
Privilege elevation
- This enhancement enables you to configure privilege elevation rules and assign them to users using the web console. You can now use the existing File Info Viewer in WEM Tool Hub to get the file information needed for rule configuration, such as, path, publisher, and hash values.
- For more information, see Privilege elevation and Manage assignments for a target.
Application security rules for WEM web console
This feature allows you to create and configure different types of application security rules and assign them to users in the web console. This feature uses the same workflow that is used for action assignments. You can now import rules configured with AppLocker to manage them in WEM. You can also use the WEM Tool Hub to retrieve information needed for rule configuration, such as path, publisher, and hash values. For more information, see Application security and File Info Viewer.
Group managed service account support for API service impersonation
- You can now use a Group Managed Service Account (gMSA) for API service impersonation, where you can either use a domain account or a gMSA to improve security. This feature now lets you use an updated UI of the WEM web console configuration tool, where you can select and configure the gMSA to the WEM API service.
- For more information, see Configure and start the Web console.
Configure multiple SPNs in a single forest for various WEM deployments
- Previously, you could create only one service principal name (SPN) for separate domains that reside in the same forest.
- With this feature, you can now configure multiple SPNs in a single forest for various WEM deployments across different domains.
- For more information, see Create a service principal name.
Rule Generator updated with expanded app access control features
- The Rule Generator for App Access Control tool now supports the expanded features of the App access control policy. With this tool, you can now create redirection rules and configure exclusions for rule assignments.
- For more information, see Rule Generator for App Access Control.
Profile Management
Workspace Environment Management now supports all supported versions of Profile Management through 2411. The following features are now available in the web console.
- App access control policy expanded. With the policy, you can now use rules to implement machine-level redirections for files, folders, and registry keys and values. In addition, You can now exclude specific users, machines, and processes from rule enforcement for more precise control.The feature is available under each configuration set in Profiles > Profile Management Settings > App access control. For more information, see Citrix Profile Management Settings.
- Folder redirection policy enhanced with more options.
- New options for redirection rule configuration:
- Redirect to the local user profile. Lets you redirect a folder to the local user profile.
- Move contents to new location. Lets you decide whether to move contents from the previous folder to the new one when setting or modifying redirection target folders.
- New option for more secured access control:
- Grant access to specific users and groups. Lets you grant specific users or groups Read & Execute permissions on the redirection target folders.
- New options for redirection rule configuration:
- Enable UWP app load acceleration. Lets you accelerate the loading of UWP apps and improve their consistency in non-persistent environments. By default, Windows stores UWP App registration data locally, which can be lost upon restart in non-persistent environments. With this policy enabled, Profile Management creates a VHDX container for each machine to store that data, improving user logon and preventing data loss on restarts.The feature is available under each configuration set in Profiles > Profile Management Settings > Advanced settings. For more information, see Citrix Profile Management Settings.
- Alert user when profile size exceeds quota. Lets you notify users when their profile size exceeds a set quota. You can customize the quota value and the notification message based on the default settings.The feature is available under each configuration set in Profiles > Profile Management Settings > Advanced settings. For more information, see Citrix Profile Management Settings.
Citrix Session Recording 2411
This release includes the following new features and addresses issues to improve the user experience:
IMPORTANT NOTE ABOUT UPGRADING TO VERSION 2411:
To prevent session recording failures due to incomplete upgrades of Session Recording agents, follow these steps when upgrading to 2411:
- Upgrade each Session Recording server to version 2411.
- Enable remote access using .NET Remoting with the following command:
<Session Recording server installation path>\Bin\SsRecUtils.exe -EnableBrokerRemoting- Upgrade each Session Recording agent to version 2411.
- After all Session Recording agents are upgraded, disable remote access using .NET Remoting with the following command:
<Session Recording server installation path>\Bin\SsRecUtils.exe -DisableBrokerRemoting
Group Managed Service Account (gMSA) support for Session Recording
Session Recording now supports Group Managed Service Accounts (gMSAs) to simplify service principal name (SPN) management for services running on multiple servers. This feature enhances security and simplifies the management of service accounts. For more information, see the best practice article: Configure Group Managed Service Accounts (gMSAs) support for Session Recording.
Support for Microsoft Entra ID authentication
In addition to SQL Server authentication, Session Recording now supports Entra ID authentication for cloud-based SQL databases including Azure SQL Database and Azure SQL Managed Instance. To enable Entra ID authentication, include the AADPASSWORD parameter and set it to 1 when installing the Session Recording database through the command line. For more information, see Install, upgrade, and uninstall.
Support for installing databases on separate Instances
You can now install the Session Recording database and Session Recording admin logging database on separate instances. To enable this feature, complete the following steps before installing the databases:
- Go to the machine where the Session Recording server is installed.
- Open the Registry Editor.
- Modify the registry:
- Navigate to
HKEY_LOCAL_MACHINE\SOFTWARE\Citrix\SmartAuditor\Server. - Add the
SmAudDatabaseLoggingStateDWORD (32-bit) value and set the value data to1. - Add the
SmAudDatabaseLoggingInstancevalue. Set the value data to the instance name where you want to install the Session Recording admin logging database.
- Navigate to
Later when you install the databases through either a GUI or command line, the admin logging database is installed on the separate instance specified by the SmAudDatabaseLoggingInstance registry value. For more information about Session Recording installation, see Install, upgrade, and uninstall.
Capturing printing activities in recorded sessions is now generally available
You can capture printing activities that occur during recorded sessions and tag them as events in recordings for later search and playback. The feature is now generally available and has been enhanced to capture the full paths of printed files. For more information, see Configure event detection policies.
Enhanced diagnostic logging
More types of diagnostic logs, beyond message queue quota exceedance, can now be detected on the Virtual Delivery Agents (VDAs) and sent to the Session Recording server. Previously, diagnostic logs were visible in the Windows Event Viewer, but they are now visible in the Session Recording web player. For more information, see View diagnostic logging.
Citrix Secure Private Access 2411
Enforce application rules based on the machine’s context
You can now enforce application access rules based on the machine’s context in addition to the user’s context. You can select the machine or user context when creating an access policy. For details, see Configure access policies for the applications.
Exclude domains from being tunneled through NetScaler Gateway
You can now configure domains that can be excluded from being intercepted and tunneled through NetScaler Gateway. You can set the app connectivity type as Internal or External to allow or exclude domains from being intercepted and tunneled respectively. For details, see Configure TCP/UDP apps.
DNS over TCP support for Secure Private Access on-premises deployments
DNS over TCP is now supported for Secure Private Access on-premises deployments. The application FQDNs can now be resolved using TCP.
Support for Secure Private Access on-premises solution on NetScaler FIPS platform
The Secure Private Access on-premises solution is now supported on NetScaler platforms that comply with Federal Information Processing Standards (FIPS) and running the 13.1–37.219 and later FIPS builds. For more information on FIPS, see Federal Information Processing Standards.
Citrix Virtual Apps and Desktops service (DaaS)
December 2024
New and enhanced features
Automated configuration tool commands for backup and restore. With this feature, you can use PowerShell commands supported by Automated configuration tool to trigger the backup and restore APIs that Studio uses. For more information, see Automated configuration tool cmdlets for backup and restore.
New permission for orphaned resource detection in Citrix DaaS. Previously, only Full Administrator or Cloud Administrator roles could perform orphaned resource detection. With the introduction of a Use Host Connection to Detect Orphaned Resources in Hypervisor permission to the Hosts category, any roles assigned with this permission can now detect orphaned resources. For more information, see Detect Orphaned Azure resources and Retrieve a list of orphaned resources.
Get started with Citrix DaaS on Google Cloud. Integrating Google Cloud Platform (GCP) with Citrix DaaS and deploying the first set of virtual desktops involves a series of sequential steps, making it a relatively intricate process. To simplify this process for administrators, a streamlined deployment experience, similar to AWS WorkSpaces Core’s Quick Deploy feature, has been introduced. This streamlined onboarding process aims to increase GCP adoption, prompting Google’s sales teams to collaborate with Citrix in customer engagements. Also, it opens avenues for Citrix sales teams to engage with customers who prioritize Google-centric solutions. For more information, see Quick Deploy for Google Cloud.
Full Configuration: Support for selecting launch template as machine profile for AWS. When provisioning AWS VMs using MCS, you can now select a launch template as the machine profile. For more information, see Select an image and a machine profile.
Multi-select policies. You can now select multiple policies and checkout the following enhancements:
- Click a policy row: If you click a policy row, the actions bar at the top shows actions of a single policy. The details pane at the bottom provides information about the policy.
- Select the check boxes of multiple policies: If you select the check boxes of multiple policies whose statuses are either enabled or disabled, then the actions bar at the top shows actions of multiple policies. The details pane at the bottom displays the number of policies selected.
NOTE:
After you select multiple policies, you can view the details of another single policy by clicking the row of that policy. This action does not clear the previously selected policies. However, the right-click action does not display the actions for that policy row.
GCP catalogs support inheriting the machine type settings from machine profiles. When creating MCS-provisioned machine catalogs in GCP environments, the machine type now defaults to the size specified in the selected machine profile. If necessary, you can manually adjust this setting. For more information, see Create a machine catalog using Full Configuration interface.
Clarity on dependent policies. Some settings are dependent on other settings. For example, a child setting might be configured, but if its parent setting is not enabled, the child setting configured does not take effect. The dependencies were not clear before. Starting with this release, clarity is provided on which are the parent policies that must be configured first before you can configure the child policies. For more information, see Policy settings.
Secure Private Access tab on Monitor. The Secure Private Access tab on Monitor provides a dedicated place for all new features related to Secure Private Access. This tab offers details on the supported functions for Secure Private Access, giving administrators a central location to access and manage these features.
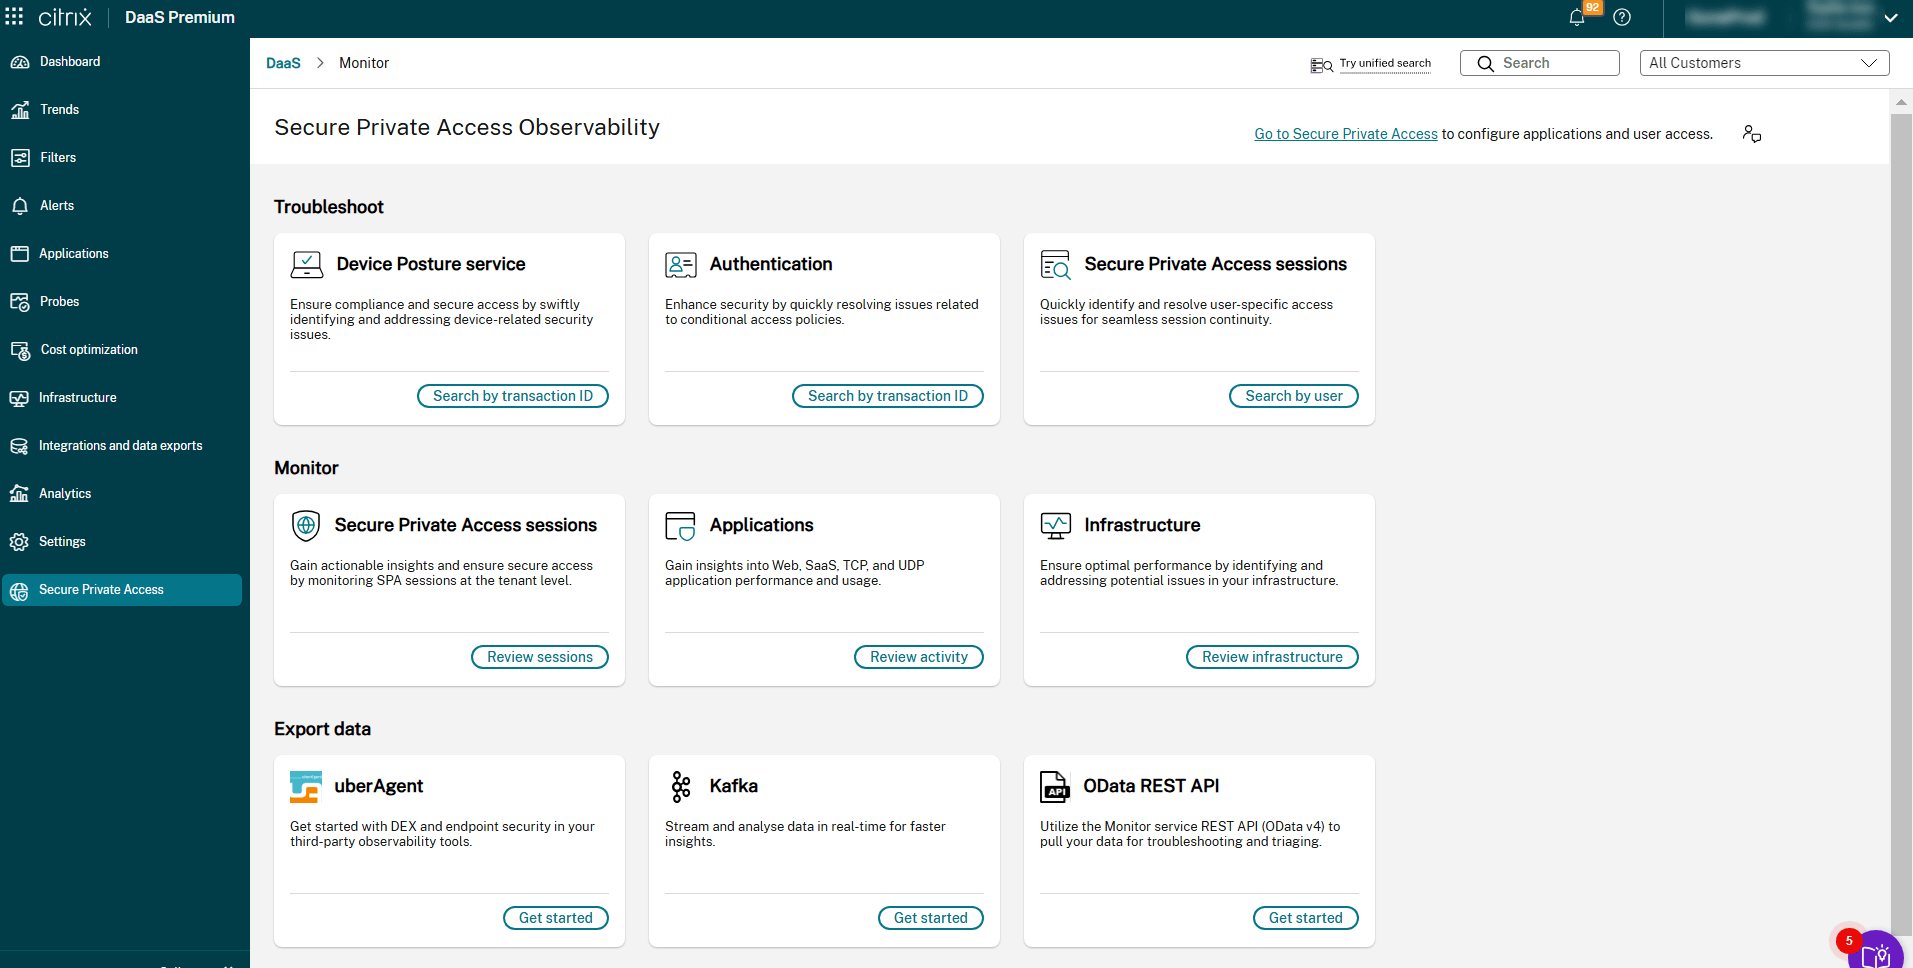
Key benefits:
- Centralized information: Administrators can easily see all supported troubleshooting features for Secure Private Access in one place.
- Enhanced observability: The new left navigation bar in the Monitor UI lists all Secure Private Access services, including Secure Private Access sessions, applications, and device posture, providing better observability.
- Improved navigation: The Secure Private Access tab includes hyperlinks to different pages, making it easier for administrators to navigate to various features and functions.
For more information, see Secure Private Access tab on Monitor.
Visibility for Secure Private Access Service. To provide detailed monitoring and visibility for Secure Private Access applications and users, Monitor is now enhanced to include Secure Private Access session visibility. The Filters tab and Dashboard provide detailed Secure Private Access session information.
Key features:
- Filter Secure Private Access Sessions: You can now filter Secure Private Access sessions in the Filters> Sessions (Web, SaaS, and TCP/UDP) tab.
- Filter Secure Private Access Applications: You can also filter Secure Private Access applications in the Filters > Applications (Web, SaaS, and TCP/UDP) tab.
- App Failures and Active Sessions: Monitor app failures for web/SaaS and TCP/UDP apps, and view active sessions for web/SaaS apps in the Dashboard.
For more information, see Visibility for Secure Private Access Service.
Unified platform experience for Citrix Monitor. Citrix Monitor is now aligned with all other components within Citrix Cloud, providing a unified platform experience. The user interface has been refreshed with a modern look and feel, offering easier navigation and better data representation. The enhanced interface is intuitive and designed to help users easily comprehend the data needed to monitor and troubleshoot Citrix sessions.
Enhancement to Connections tab. The Connections tab now offers streamlined navigation for quicker troubleshooting. From the Filters tab > Connections page, you can directly access:
- Activity Manager: Click the Associated User or Endpoint name to view the respective Activity Manager details.
- Machine Details page: Click Machine Names to see comprehensive machine information, including machine details, utilization details, infrastructure details, and applied hotfixes. For more information, see Troubleshoot Machines. This enhancement simplifies navigation, enabling faster resolution of connection-related issues.
For more information, see Filter data to troubleshoot failures.
Filter resource location details. You can now view the resource location for single-session or multi-session OS machines in the Filters > Machines tab. This enhancement allows you to quickly identify and address issues related to specific resource locations, leading to a smoother user experience.
To display the new Resource Location column, go to Choose Columns and select Resource Location in the Filters > Machines tab.
Enhancement to Session Performance tab. The Session Topology section of the Session Performancetab is enhanced to include the following endpoint metrics which exist in the Citrix Workspace app for Windows, Mac, Linux, HTML5, or Chrome:
- Public IP address
- Internet Service Provider
- Location such as country or city
- Whether the Citrix Workspace app session is opened in native app or browser (HTML5)
- Accessed using Workspace or StoreFront
- Resource utilization such as CPU %, Memory %, and GPU (Overall %)
- Network latency
This enhancement helps to troubleshoot issues regarding sessions quickly. For more information, see Session Performance metrics.
Machine net active usage. The Workload rightsizing page now includes detailed insights into machine net active usage, providing the following details:
- Percentage of net active usage
- Average machine uptime
- No session time
- Idle time
- Disconnected time
This feature allows you to see detailed machine usage information, enabling you to optimize costs accordingly.
For more information, see Workload rightsizing.
Cloud Connector health monitoring. The Cloud Connector component is now added to the Infrastructure Monitoring dashboard. Cloud Connectors are automatically onboarded when a connection between Citrix Cloud and your resource locations is established.
This feature enables administrators to monitor the health of Cloud Connectors using a single dashboard view and proactively configure alerts.
NOTE:
The
citrixinframonitor.msiis not required to be installed for monitoring Cloud Connectors.
Benefits:
- Comprehensive monitoring: Visibility into critical health indicators for the Cloud Connector such as high availability, connection lease exchange, and AD provider, and so on
- Configurable alerts: You can configure alerts on health metrics of interest, define severity, and scopes for admins to receive detailed alerts according to the alert configuration.
To monitor the Cloud Connector, click the Infrastructure tab on Monitor. The Infrastructure Monitoringpage opens.
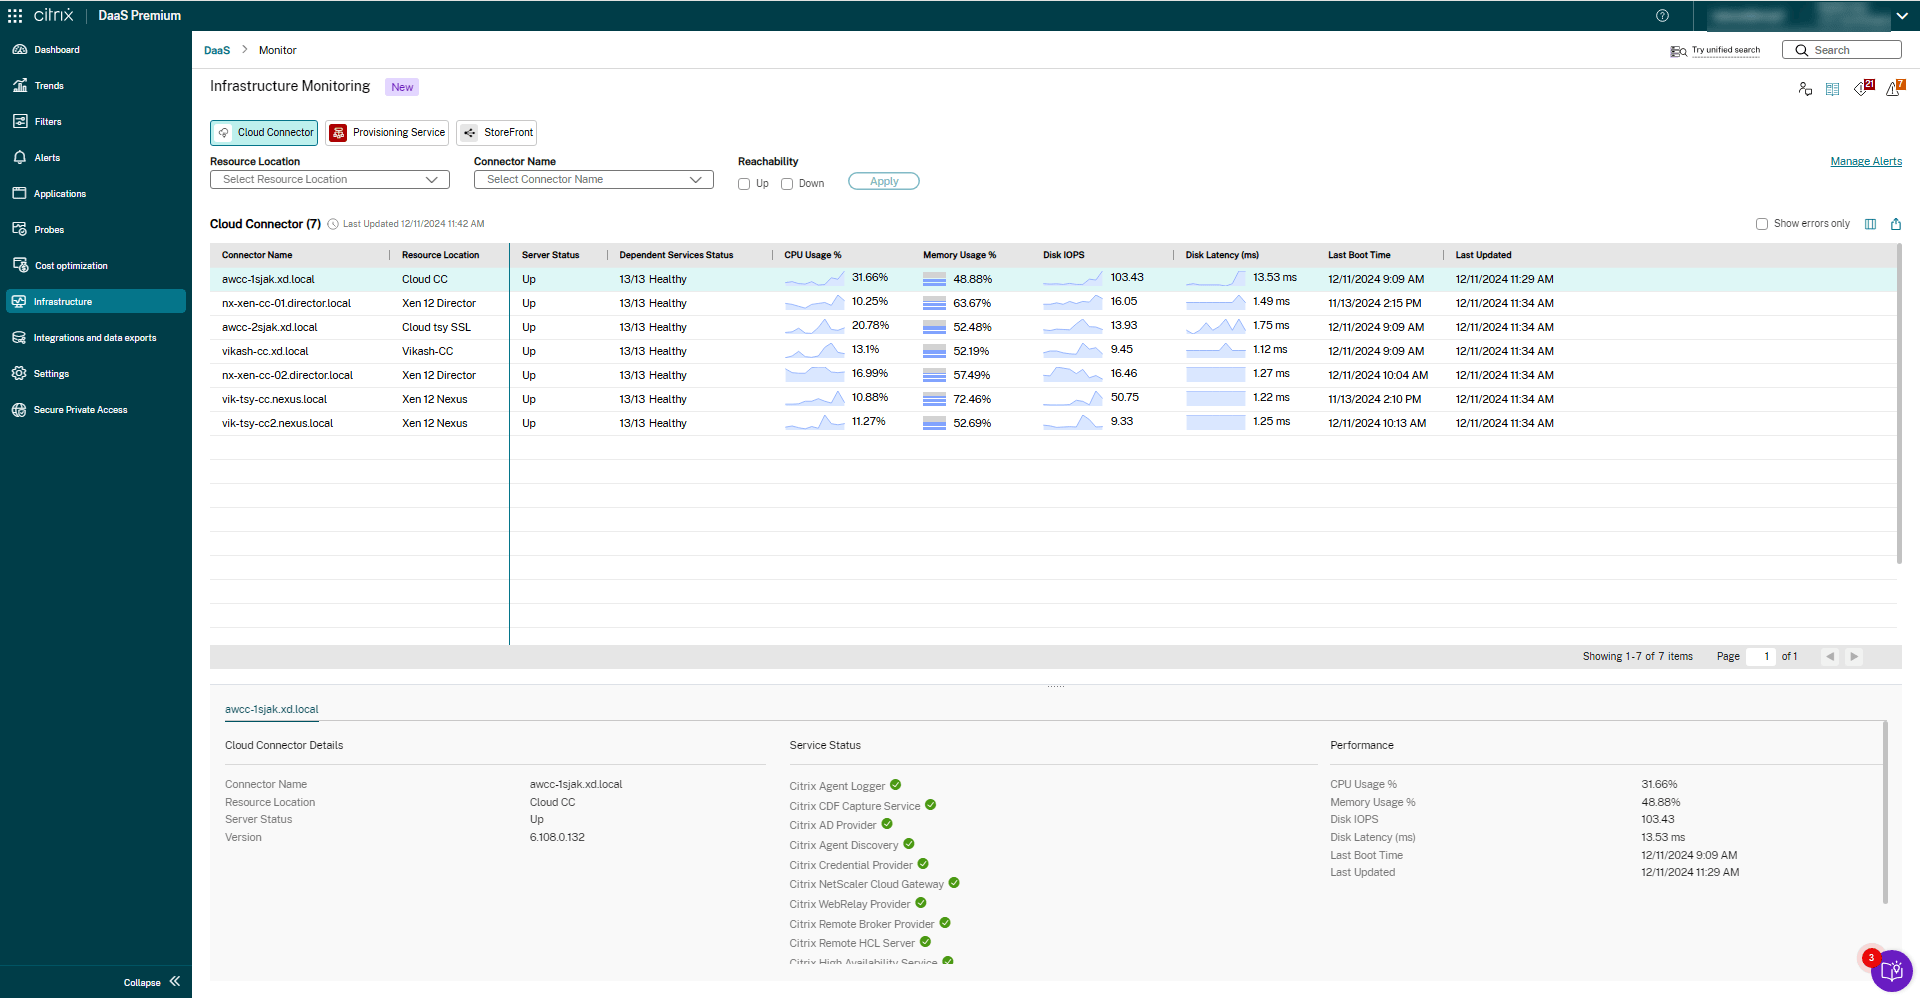
You can also view the details of all the services status in the Cloud Connector Details section.For more information, see Cloud Connector health metrics.
Support for creating Citrix Provisioning catalogs in VMware environments using Studio. With Studio, you can now create Citrix Provisioning catalogs in VMware environments. Previously, you had to switch between different consoles to provision and manage those catalogs. This feature simplifies the process, letting you perform provisioning and power management tasks entirely within Studio. For more information see, Create a Citrix Provisioning catalog in VMware environment using Studio.
Delivery of app attach disks as CimFS. Previously, only delivery of app attach disks as virtual disks (VHD and VHDX) was supported. With this feature, delivery of app attach disks as Composite Image File System (CimFS) is also supported. For information, see Store application packages on network shares.
Optimize storage load balancing with the least load method. Previously, Machine Creation Services (MCS) used a round-robin method to distribute VMs across storage repositories, often leading to uneven storage utilization.
Studio now introduces the Optimize storage load balancing with least load method option. If you select two or more OS data storage locations during catalog creation, this option becomes available, enabling disks to be allocated to the least loaded storage repository.
This feature enhances load balancing and improves system stability, and it’s supported in XenServer, VMware, and SCVMM virtualization environments. For more information, see Step 3. Storage selection.
Support for NVMe-only SKUs in Azure. Previously, MCS supported only SCSI storage controller type. With this feature, MCS also supports the NVMe storage controller type to support the new VM SKUs on Azure. For information on NVMe, see the Microsoft documentation General FAQ for NVMe. For information on creating an MCS machine catalog using a service offering that:
- supports both SCSI and NVMe, see Create a catalog using a service offering that supports both SCSI and NVMe
- supports only NVMe, see Create a catalog using a service offering that supports only NVMe
Set a default time zone for your Citrix DaaS site. With Studio, you can now set a default time zone for your Citrix DaaS site. To complete this task, go to Settings > Date and Time. Studio uses this time zone for all time displays and scheduling such as scheduled restart and autoscaling. This setting makes it easier to manage time and ensure time consistency across your site. For more information, see Time zone setup.
If needed, you can change the time zone for individual resources. For example, you can set a different time zone for a delivery group that serves machines in a different region. For more information, see Change user settings in a delivery group.
Studio aligns with Citrix Cloud’s unified navigation experience. As part of the shift towards a unified navigation experience across the Citrix Cloud platform, we’ve updated Studio to align with this platform-wide initiative. Key changes include a green background for the navigation pane and breadcrumb navigation for easier access. These updates enhance usability and drive feature adoption, making it easier to discover and manage resources. For more information, see Studio.
Support for AWS on-demand provisioning. Previously, when you would shut down a non-persistent VM in AWS, the OS disk did not get deleted. Now, with on-demand provisioning, the OS disk gets deleted when you shut down a non-persistent VM. This implementation of AWS on-demand provisioning saves cost when the VM is not in use. For more information, see AWS on-demand provisioning.
Show Secure Default Settings. This feature shows the secure default setting along with the default setting for a policy. The default setting might be overwritten by the secure default setting. If the secure default setting is enabled, during VDA installation, the priority of the policy settings is affected as follows:
- Customized setting takes the highest priority
- Secure default setting takes the second priority
- Default setting takes the least priority
For more information, see Policy settings.
Displaying policy details in Device Posture Events. You can now view Device Posture policy evaluation details as part of Device Posture events on Citrix DaaS Monitor. The different states of the policy evaluation and error codes are displayed. This feature simplifies the triage and troubleshooting of user issues. For more information, see the Diagnose Device Posture events failure page.
November 2024
New and enhanced features
Image management is now Generally Available. Image management functionality is now generally available for Azure and VMware virtualization environments. Also, the Images node now allows you to share image versions across hosting units within the same hosting connection in Azure. This implementation ensures consistency and uniformity of images across different host units, enhancing deployment flexibility and operational efficiency. You can also use PowerShell commands to achieve this goal. For more information, see Image Management.
WebSocket communication. With this feature, you can set up a WebSocket connection for communication between VDAs and Delivery controllers as an alternative to using WCF communication. For more information, see WebSocket communication between VDA and Delivery Controller.
Studio support for a snapshot of the disk or an OS image of the disk as a master image in the GCP. In the GCP virtualization environment, you can now select a snapshot of the disk or an image of the disk as a master image while using Studio to create an MCS machine catalog. The snapshot of the disk or an image of the disk can be regional and multi-regional as compared to the VM instance which is only regional. This feature significantly simplifies image management workflow and reduces the time and effort required for image management in GCP. For information on creating an MCS catalog in GCP using Studio, see Create a machine catalog.
Connecting Citrix Components from the UI. Admins can use the Monitor UI to register their Citrix components for Infrastructure Monitoring. After installing Citrixinframonitor.msi, the UI-based workflow can be used to complete the registration process without needing to use PowerShell commands. This enhancement simplifies the process of registering, deregistering, and updating Citrix components.
The new Connect Citrix components page allows you to manage connections between Citrix components and the Citrix DaaS site. You can also view the available connections from Provisioning Service and StoreFront on this page.
These updates streamline the management and integration of Citrix components, making it easier to maintain and monitor your infrastructure.
For more information, see Step 2: Register Citrix Infrastructure Monitor on Monitor UI.
Enhancement to Advanced Alert Policies. Alerts related to Infrastructure Monitoring, previously known as Infrastructure policies, are now part of Advanced alert policies.
You can select the dependent services based on the selected data source and create alerts for Cloud Connectors as well.
NOTE:
The existing Infrastructure policies created for Provisioning Service and StoreFront are migrated to the Advanced alert policies section.
For more information, see Advanced alert policies.
Support to configure secondary VMs scale up or scale down list for MCS-created catalogs on Azure.Web Studio now enables the administrators to define secondary VMs to scale up and scale down the MCS-created catalogs on Azure. Based on the usage of CPU and memory resources, if the CPU or memory usage exceeds a certain threshold, the system will automatically use the secondary VMs to handle the load. Alternatively, if the usage falls below a certain level, the system will automatically shut down some VMs to conserve resources. For more information, see Create a machine catalog using an Azure Resource Manager image in Studio.
Delivery group details enhanced with policy information. We’ve enhanced the Details view for Delivery Groups by adding a dedicated tab that shows policies assigned to the selected group. This improvement simplifies policy management, configuration, and troubleshooting for delivery groups by providing quick access to relevant policy information.
Support for multi-region snapshot of the disk or an image of the disk as master image in GCP. A snapshot or an image of a disk in GCP can be regional or multi-regional. Regional snapshots and disk images are tied to a particular region, example, us-central1, whereas multi-regional snapshots and disk images are tied to a geo-location, example, US. With this feature, you can use a multi-region snapshot of the OS disk or an image of the disk as master image input when creating MCS machine catalogs in GCP. You can see the list of all snapshots (both regional and multi-regional) under snapshots.folder location and disk images (both regional and multi-regional) under images.folder under hosting unit inventory path.
Support for converting a non-machine profile-based machine catalog to machine profile-based machine catalog in VMware environment. In the VMware environment, you can now use a VMware template as a machine profile input to convert a non-machine profile-based machine catalog to a machine profile-based machine catalog. New VMs added to the catalog take property values from the machine profile. For more information, see Convert a non-machine profile-based machine catalog to machine profile-based machine catalog.
Support for Windows Server 2025. Citrix Virtual Apps and Desktops now supports Windows Server 2025. For more information on Windows Server 2025, see the Microsoft documentation What’s new in Windows Server 2025.
Studio: Support for provisioning persistent VMs on Windows Server OS using Full Copy Clone. Studio now supports provisioning persistent VMs on Windows Server OS using the Full Copy Clone approach. This approach improves data recovery and migration capabilities and can help reduce IOPS after machines are created. For more information, see Select a desktop experience and Virtual machine copy mode.
Studio AWS Quick Deploy: Support for adding non-BYOL-enabled AWS accounts. Studio now allows you to connect an AWS account without enabling BYOL feature for a region. You can configure the BYOL feature for a region later. The account without BYOL enabled for a region has a restriction of selecting only default tenancy images and shared directory connection to continue to setup the account. For more information, see Connect your AWS account.
Backup and restore using Studio is now Generally Available. You can now use the Backup and Restore node available in the left pane of your Manage DaaS console. This feature enables you to create on-demand and scheduled backups and restore deleted applications, policies, and more. For more information, see Backup and Restore using Studio.
Configuration guides widget on the Studio Home Page. We’ve updated the Studio Home page by renaming the Get started widget to Configuration guides. This widget now includes the original Get Started with DaaS guide and a new Check resiliency configurations guide.
Check resiliency configurations guide. We’ve introduced a new Check resiliency configurations guide in the Configuration guides widget on the Studio Home page. This guide provides checklists for verifying resiliency settings across various types of StoreFront deployments:
- Checklist for on-premises StoreFront deployments
- Checklist for Cloud StoreFront deployments
- Checklist for mixed StoreFront deployments
Following this guide, you can verify Local Host Cache and Service Continuity are properly configured in your deployment, ensuring uninterrupted access to apps and desktops during service disruptions.
DaaS get-started guide now generally available. The Get-started with DaaS guide streamlines and simplifies the DaaS deployment process for both new and experienced administrators. This guide walks you through setting up your DaaS deployment by asking a series of questions to guide the configuration. For more information, see Use DaaS get-started guide.
Enhanced domain selection. A new option in the UI now allows you to enter a domain name for an exact match wherever domain selection is needed. This enhancement offers these benefits:
- Faster searches: You can skip browsing large directories, getting results directly and instantly.
- Time savings: Eliminates full-directory loading, speeding up workflows.
- Enhanced experience: Improves admin management efficiency, especially in environments with large directories.
Validate configuration before creating an MCS machine catalog in AWS environments. With this feature, you can now validate configuration settings before creating an MCS machine catalog in AWS environments using the parameter -validate in New-ProvScheme command. After you run this PowerShell command with the parameter, you get an appropriate error message if there’s an incorrect parameter used or a parameter has conflict with another parameter. You can then use the error message to resolve the issue and successfully create an MCS machine catalog using PowerShell. This feature is applicable to AWS, Azure, GCP, and VMware virtualization environments. For more information, see Validate configuration before creating an MCS machine catalog.
Update to Performance Metrics panel. The Performance Metrics panel has an enhanced visualization of the historical data metrics. When you click the Session Performance tab, along with the last 15-minutes data, you can view the last 48 hours data for ICARTT and ICA Latency. This enhancement helps to reduce mean time for resolution by enabling admins to triage issues even though the session was terminated in the last 48 hours.
For more information, see the Performance metrics section.
Enhancement to Filters tab. With this release, the following extra filters are added to the Sessions tab.
- All – Displays all sessions
- Active, Connected, and Disconnected – Displays only the active, connected, and disconnected sessions.
- Ended – Displays only the sessions that have ended within the last 48 hours. The default filter is Active, Connected, and Disconnected.
Enhancement to ended session [Preview]. In the ended session (formerly historical session), the Session Performance tab shows data for the last 48 hours. Also, you can view the Session Logon tab for the ended session.
For more information, see the Diagnose ended user sessions [Preview] page.
October 2024
New and enhanced features
Policy sets now generally available. Policy sets are collections of rules and guidelines that allow simplified, role-based, and easy management operations. Policy sets allow you to create logical divisions within your administrator team, organizations, or machines. You can assign scopes and delivery groups so that authorized administrators can manage the relevant policies for users and machines. For more information, see Policy sets.
Enroll persistent machines of hybrid Azure AD joined type into Microsoft Intune for co-management. During machine catalog creation, you can now enroll persistent machines of the hybrid Azure AD joined type into Microsoft Intune (with Configuration Manager) for co-management. This feature applies to single and multi-session, persistent VMs and on all hypervisors and cloud services, ensuring uniform device management across your infrastructure. This feature is applicable only to VDA version 2407 and later.
For more information, see Hybrid Azure AD joined catalogs enrolled in Microsoft Intune and Create Hybrid Azure AD joined catalogs enrolled in Microsoft Intune.
Diagnose conditional authentication failures. Whenever any conditional authentication fails, you can use the transaction ID available in the failure message and search in the Monitor for the failure details. Monitor helps you to troubleshoot conditional authentication failure events by displaying failure reasons and conditional policies on the Monitor UI. For more information, see Diagnose conditional authentication failures.
Service accounts for machine identity management. MCS has developed a new mechanism for managing on-premises Active Directory and Azure Active Directory (Azure AD) identity service accounts to simplify and enhance the management of machine identities including computer accounts in on-premises Active Directory, Azure AD joined devices and Intune enrolled devices. Firstly, we have introduced on-premises Active Directory service account support which allows administrators to manage computer accounts in on-premises Active Directory without having to enter domain credentials every time. Secondly, we have introduced Azure AD identity Service Principal Names (SPN) support which allows administrators to manage Azure AD joined or Intune enrolled devices in the Azure AD tenant, in a secure and streamlined manner. Lastly, we have implemented a new mechanism for service account management in our Studio, simplifying the process and making it easier to maintain security and compliance. For more information, see Service accounts for machine identity management.
Support to select an Instance template as a machine profile. When creating MCS machine catalogs in GCP environments using Studio, you can now select Instance Templates as the inputs for machine profiles. Also, the Customer-Managed Encryption Key (CMEK) settings follow a priority sequence. For more information, see Create a machine catalog using Studio
Export a machine profile to an ARM template spec. Studio now supports exporting the machine profile used by a catalog into an ARM template spec. With this feature you can easily reuse an existing machine profile as a template and modify it for future provisioning needs. For more details, see Export a machine profile as an ARM template spec.
MCS catalogs: AWS launch templates support. You can now use AWS launch templates as machine profiles when creating or editing MCS catalogs in your AWS environment. AWS launch templates are available in the machine profile list for selection.
Retrieve Connector Appliance information. With this feature, you can use the PowerShell command Get-ConfigEdgeServer to retrieve the Connector Appliance information.
Get-ConfigEdgeServer -ConnectorType 'Unified': Returns Connector Appliance informationGet-ConfigEdgeServer -ConnectorType 'Windows': Returns only edge servers informationGet-ConfigEdgeServer: Returns only edge servers information.
Reboot schedules for hibernated VMs. With this feature, you can configure reboot schedules for hibernated VMs if the Delivery Group is hibernation enabled. In the reboot cycle, the VMs are resumed and, then shut down. The reboot schedule can be set as weekly, daily, monthly, and once. You can configure multiple schedules. Note that VMs resuming from hibernation can take few mins.
Data caching for the Images node. We’ve introduced data caching for the Images node to improve the overall user experience. This enhancement significantly reduces the page load time when you navigate to the Image definition and Image versions lists, as well as the Details and Image Scheme tabs.
Configuration logs labeling. You can now label configuration logs on the Logs > Events tab, facilitating the identifying and exporting of logs. In addition, the Logging node now offers enhanced features, including exporting logs to CSV files, advanced search, and table-style display for the Events tab. For more information, see View configuration log content.
Support for creating a host connection using Azure Managed Identity. Previously, you could create an Azure hosting connection using a service principal. This required providing and storing of the application ID and secret of the service principal. The Azure Managed Identities offers a secure and scalable way to access Azure services without the need to manage credentials. This approach eliminates the risks associated with storing, rotating, and managing secrets. Managed identities also support automatic token refresh, ensuring that applications always use valid credentials without any additional code for token lifecycle management.
With this feature, you can create a host connection to Microsoft Azure Resource Manager using Azure Managed Identity. Currently, you can create the host connection using only PowerShell commands. For information on creating a host connection using Azure Managed Identity, see Create a host connection using Azure Managed Identity.
Support for Boot Integrity Monitoring in Azure. With this feature, in Azure virtualization environments, you can enable Boot Integrity Monitoring for MCS machine catalog VMs (persistent and non-persistent VMs) using a machine profile (VM or template spec) that has GuestAttenstation extension installed. Boot Integrity Monitoring is only supported for Trusted Launch and Confidential VMs that use Secure Boot and virtual Trusted Platform Module(vTPM).
If your VM has Secure Boot and vTPM enabled, and GuestAttestation extension installed, Microsoft Defender for Cloud can remotely validate that your VM boots correctly. This monitoring is called Boot Integrity Monitoring. For more information on boot integrity monitoring, see Boot integrity monitoring overview.
For information on creating a catalog enabled with boot integrity monitoring, see Boot Integrity Monitoring.
Filter empty resource groups. With this feature, you can filter out empty resource groups while selecting a master image, machine profile, or prepared image during the machine catalog creation. You can do this using a PowerShell command Get-HypInventoryItem. For more information, see Filter empty resource groups.
Support for creating preformatted WBC disk catalogs in Azure. With this feature, in Azure virtualization environments, you are able to utilize a preformatted WBC disk for newly created catalogs. This action significantly reduces the time required to start each VM of an MCS or MCS provisioned Citrix Provisioning machine catalog. To implement this functionality, create an Azure catalog with WBC enabled and include an additional custom property PreformatWriteBackCache as True.
You can update an existing catalog using the Set-ProvScheme command to update the WBC disk size.
This feature is compatible with the Image management workflow where MCS separates the mastering phase from the overall provisioning workflow. For more information, see Create a preformatted WBC disk catalog.
Delete WBC disk at shutdown for MCS provisioned Citrix Provisioning catalogs. With this feature, you have the option to delete the write-back cache (WBC) disk after you shut down the VM for MCS provisioned Citrix Provisioning catalogs in Azure. This implementation helps to save cost when you do not need a persistent WBC disk. This feature is also applicable to an existing catalog. For more information, see Delete WBC disk at shutdown for MCS provisioned Citrix Provisioning catalogs.
Support for creating a network security group. With this feature, you can now create a Deny-All network security group for image preparation instead of requesting Citrix to create and modify a network security group automatically. Edit the custom properties of the hosting unit using a PowerShell command Set-Item to include the parameter NsgForPreparation to provide the Deny-All network security group. For more information on using the PowerShell command, see Use a pre-created network security group.
Support for using Azure temporary disk as a WBC disk for existing MCS machine catalogs. With this feature, you can now use Azure Temporary disk as a write-back cache (WBC) disk for existing MCS machine catalogs and existing VMs. Use the Set-ProvScheme PowerShell command to update existing catalogs. This implementation saves storage cost because Azure temporary disk is free of charge. For information on the steps, see Use temporary disk as WBC disk for existing catalogs.
Errors and warnings center. With a new widget, Errors and warnings, on the Studio Home page, you can now view all errors and warnings from your DaaS deployments in one place. This widget streamlines issue resolution by consolidating scattered alerts, enhancing visibility, and reducing troubleshooting time. For more information, see Home page.

Enhancement to Trends page. The Trends page now features two new banners linking to the Cost optimization page, providing quicker access to cost-saving information and reports. The Machine Usagetab now includes links to Estimated Savings and Savings report, while the Resource Utilization tab offers a link to Workload rightsizing (formerly known as Infrastructure rightsizing). These enhancements streamline navigation and improve visibility, enabling users to make data-driven decisions for cost optimization. For more information, see the Trends page.
Citrix Workspace App – Target release dates for desktop apps
| Citrix Workspace app | Feb 2024 | Mar 2024 | Apr 2024 | May 2024 | Jun 2024 | Jul 2024 | Aug 2024 | Sep 2024 | Oct 2024 | Nov 2024 | Dec 2024 |
|---|---|---|---|---|---|---|---|---|---|---|---|
| Windows | – | – | ☑ | – | – | ☑ | ✲ | ☑ | ✲ | – | ☑ |
| Windows LTSR | ◇ | – | ☑ | – | ◇ | – | – | ◇ | – | – | ◇ |
| Mac | – | – | ☑ | ✲ | – | ☑ | ✲ | ☑ | ✲ | – | ☑ |
| ChromeOS and HTML5 | ☑ | – | ☑ | ☑ | ☑ | – | ☑ | ✲ | – | ☑ | ✲ |
| Linux | – | ☑ | – | ☑ | – | – | ☑ | – | – | ☑ | – |
| Note: The ☑ symbol denotes major releases and the ✲ symbol denotes minor releases. The ◇ symbol denotes cumilative updates (CUs). | |||||||||||
Citrix Workspace App – Target release dates for mobile and tablet apps
Citrix Workspace app for Android and Citrix Workspace app for iOS follow a monthly release cadence.
| Citrix Workspace app | Mar 2024 | Apr 2024 | May 2024 | Jun 2024 | Jul 2024 | Aug 2024 | Sep 2024 | Oct 2024 | Nov 2024 | Dec 2024 |
|---|---|---|---|---|---|---|---|---|---|---|
| Android and iOS | ☑ | ✲ | ☑ | ✲ | ☑ | ✲ | ☑ | ✲ | ☑ | ✲ |
| Note: The ☑ symbol denotes major releases and the ✲ symbol denotes minor releases. Minor releases are optional releases tailored to meet specific requirements or improvements. | ||||||||||
Citrix Workspace App 2409 for Windows
- Support for Windows 11 24H2
- Feature flag management
- Single sign-on support for Edge WebView when using Microsoft Entra ID
- Enhanced virtual desktop screen resizing experience
- Enhanced desktop launch experience
- Enhancement to sustainability initiative
- Streamlined beacon checks
- .NET requirements
- SOCKS5 proxy support for EDT
- Customization of Desktop Viewer toolbar
- Remember USB connections
- Disabling the “Exiting Full Screen Mode” tip prompt
- Support for WebHID API in UCSDK
- Support for TLS protocol version 1.3
- Disabling TLS 1.0 or 1.1 communication protocols
- Default audio device selection
- Connection Strength Indicator on Desktop Viewer toolbar
- Enable Audio Quality Enhancer to improve audio performance (Technical Preview)
- Virtual Channel Plugin Manager
- Deprecation of HDX RealTime Optimization Pack for Skype for Business
Citrix Workspace App 24.12 for iOS
- Launch of in-memory ICA solution
- Fast smart card
- Support for WSUI on-premises using gateway
- Enforcing Citrix access using Citrix Workspace app
- Support for multi-site store failover based on geo-location
- Right option key mapping for Alt key
- Connection Strength Indicator
- Enhanced new customizable toolbar
- Deprecation of operating system iOS 15
Citrix Workspace App 24.11 for Linux
- Supporting Linux distributions
- NFC support for FIDO2 authentication (Technical Preview)
- Echo cancellation
- Noise suppression
- Connection Strength Indicator on Desktop Viewer toolbar (Technical Preview)
- Enhanced desktop launch and screen resizing experience
- Multi-monitor layout selection (Technical Preview)
- Audio Quality Enhancer for Adaptive Audio (Technical Preview)
- Sustainability initiative from Citrix Workspace app
- Bidirectional content redirection
- HDX direct
- Customization of Desktop Viewer toolbar
- Support for WebHID API in UCSDK
- Support synchronizing Swedish keyboard layout
Citrix Workspace App 24.09 for Android
- Supports GACS authenticated microservices (Cloud)
- Enhanced EDT congestion control
- Support for more than one session on Samsung DeX with Samsung Knox
Citrix Workspace App 2411 for Apple MacOS
- Enhancing Citrix security with pre-populated user name
- Version control using MDM and GACS
- Auto updates support scheduling
- Auto-update enhancement for active users
- UCSDK HID Implementation
- Enhanced keyboard and IME diagnostics tool
- HDX Direct
- Support for log collection when session launch fails
- Support for plug and play webcam redirection
- Support for browser content redirection (Technical Preview)
- Enhanced display control with Multi-Monitor selector (Technical Preview)
- USB Redirection of mass storage devices (Technical Preview)
- HDX Direct for non-shield scenario (Technical Preview)
- Enable Audio Quality Enhancer to improve audio performance (Technical Preview)
- Mandate end users to authenticate and access apps and desktops through native app
- Auto-update support for user groups
Citrix Workspace App 2411 for HTML5
- Enhanced desktop launch experience
- Enhanced virtual desktop screen resizing experience
- Enhanced session reliability
- Improved in-session toolbar
- Sustainability initiative from Citrix Workspace app
- Enhanced log collection
- Enhanced troubleshooting with endpoint telemetry in Citrix Director
- Progressive Web App version of Citrix Workspace app for HTML5 for StoreFront
- Citrix VDA for macOS – clipboard and keyboard shortcuts
- Enhanced keyboard and IME diagnostics tool
Citrix Workspace App 2411 for Chrome OS
- Scanner redirection support
- Enhanced session reliability
- Enhanced desktop launch experience
- Enhanced virtual desktop screen resizing experience
- Support for HTTP Proxy
- Improved in-session toolbar
- Sustainability initiative from Citrix Workspace app – Customize the sustainability message
- Enhanced troubleshooting with endpoint telemetry in Citrix Director
- Citrix VDA for macOS – clipboard and keyboard shortcuts
- Enhanced log collection
- Enhanced keyboard and IME diagnostics tool
- Enhanced display control with multi-monitor selector
Source
docs.citrix.com